
SAP BTP Principal Propagation Explained
Single sign on is valuable when it improves user experience and strengthens assurance at the same time. The design must match the access channel, supported protocol, identity source, trust model and operational responsibility.
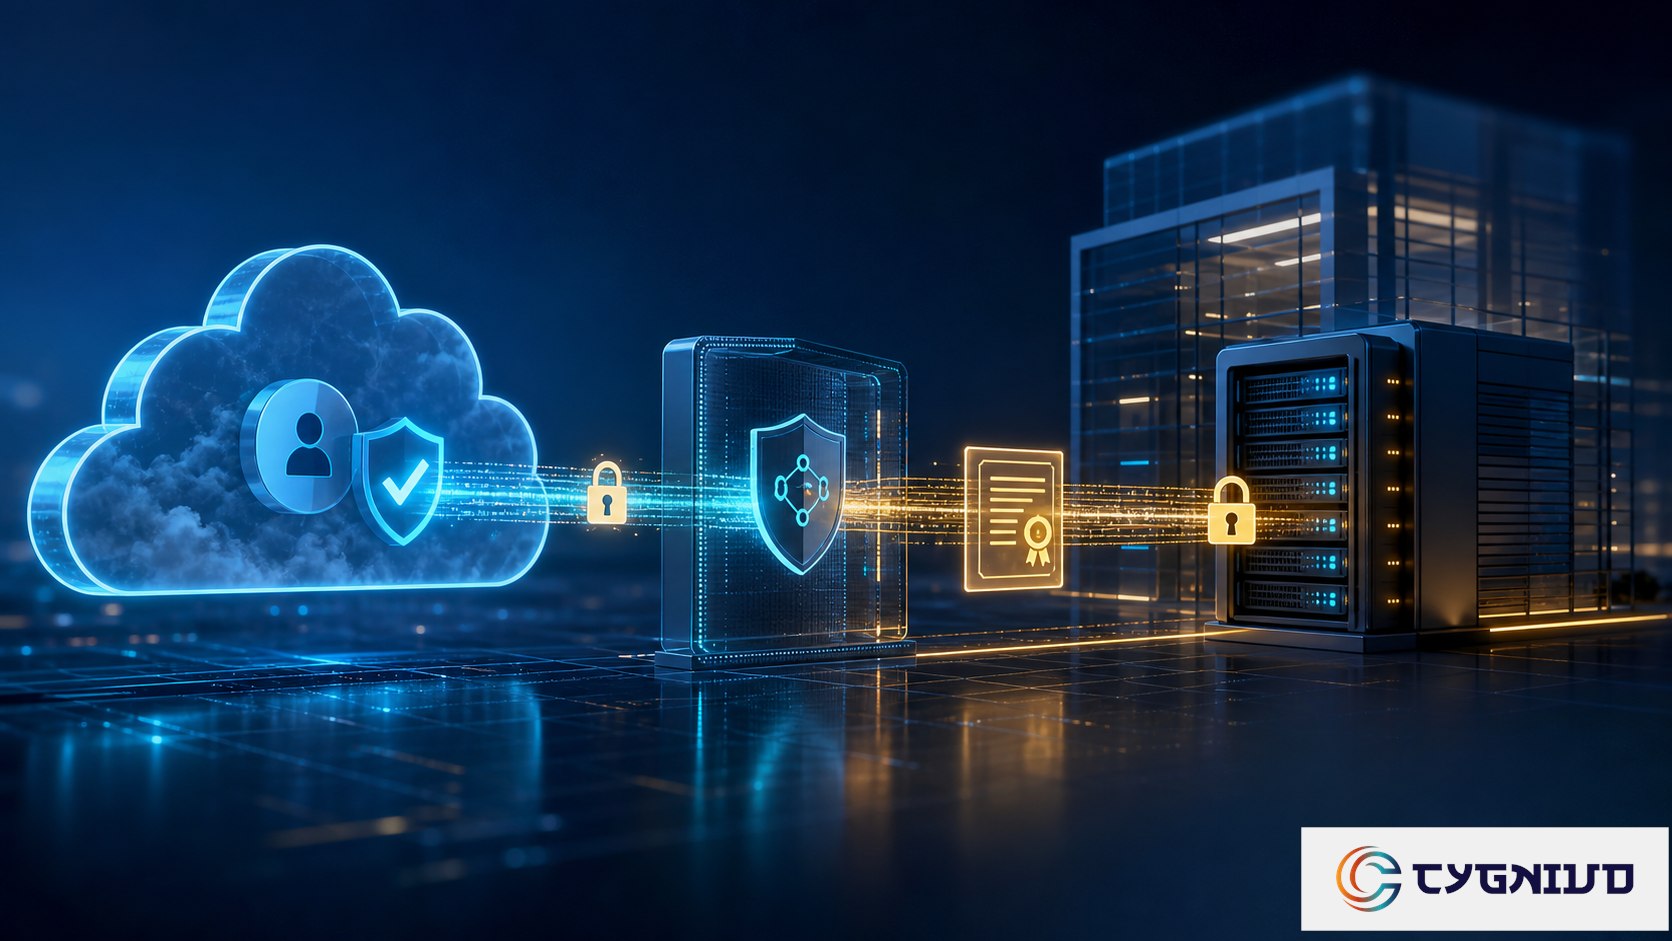
SAP BTP Principal Propagation Explained explains secure forwarding of an authenticated cloud user identity to an on premises SAP system without asking the user for another password. It is particularly relevant for SAP BTP applications that call ABAP services on behalf of the signed in user. The objective is not merely to remove a password prompt. It is to create a traceable authentication path that proves the right identity, protects the session and supports reliable authorization inside SAP.
What this SAP authentication method does
Authentication establishes who is requesting access. Single sign on reuses an existing trusted authentication result so the user does not repeatedly enter credentials. Authorization remains a separate SAP responsibility. The mapped SAP user still requires appropriate roles, organizational restrictions and segregation of duties controls.
Secure forwarding of an authenticated cloud user identity to an on premises SAP system without asking the user for another password. A sound design records every trust relationship, token or credential lifetime, identity mapping rule, fallback path and operating owner. This prevents a convenient login experience from hiding weak accountability.
Where the method fits in an SAP landscape
SAP GUI, browser applications, cloud services and application integrations use different communication patterns. Desktop SAP GUI commonly relies on Secure Network Communication with Kerberos or X.509 credentials. Browser applications typically use federation standards such as SAML 2.0 or OpenID Connect. Hybrid applications can preserve user context through principal propagation. Technical integrations normally need a service identity rather than an interactive user identity.
The method described here fits SAP BTP applications that call ABAP services on behalf of the signed in user. Teams should confirm product support and the exact system release before finalizing architecture. They should also distinguish a currently recommended pattern from a legacy option that remains only because an older component still depends on it.
End to end authentication flow
The flow begins when a user or application presents evidence to a trusted identity service. That service verifies the evidence according to policy, which can include domain authentication, a certificate, a security key, a biometric, a time based code or another approved factor. The resulting token or certificate must be limited to its intended audience and protected against replay or substitution.
The SAP entry point validates the trusted result and maps the external identity to exactly one SAP user. The SAP system then evaluates authorization for the requested business action. Logging should preserve enough context to connect the identity provider event, the authentication credential, the mapped SAP account and the resulting business session.
Architecture decisions
The design should cover identity provider trust, destination design, Cloud Connector trust, backend mapping, authorization, traceability. Each decision needs an accountable role and evidence that can be reviewed before the method is enabled for production users.
| Decision area | Accountable participants | Evidence required |
|---|---|---|
| Identity provider trust | Business and identity owner | Approved design and acceptance evidence |
| Destination design | SAP security and architecture | Validated trust, mapping and security result |
| Cloud Connector trust | SAP Basis and operations | Operational procedure and monitoring evidence |
| Backend mapping | Risk and control owner | Decision record with owner and review date |
| Authorization | Business and identity owner | Approved design and acceptance evidence |
| Traceability | SAP security and architecture | Validated trust, mapping and security result |
Security and zero trust controls
Single sign on does not mean permanent trust. Apply explicit verification at the identity provider, protect credentials and private keys, limit token lifetime, validate the target audience and monitor unusual authentication behavior. High privilege roles can require stronger factors, shorter sessions and additional approval before sensitive activity.
Fallback access deserves the same scrutiny as the primary method. A local password that is retained for recovery can become the easiest attack route if it is not protected, monitored and reviewed. Emergency access should have a defined owner, strong proof, time limitation and complete activity evidence.
- Technical user impersonation: establish an explicit control, accountable owner and measurable review condition.
- Identity loss across hops: test the complete authentication path and preserve evidence before wider deployment.
- Mapping mismatch: remove ambiguous fallback and document the approved recovery method.
- Overbroad backend access: monitor the condition continuously and give every exception an expiry date.
Identity mapping and SAP authorization
Identity mapping is the bridge between the external identity and the SAP account. Select an attribute that is unique, stable and governed through the employee or partner lifecycle. Avoid mappings that can be reassigned without control. Test case sensitivity, name changes, mergers, contractors, shared devices and users with several SAP accounts.
After authentication, SAP authorization determines what the user can do. Review roles, privileged access, emergency accounts and segregation of duties as part of the implementation. A successful authentication to an incorrectly mapped or overprivileged account is a control failure, even when the protocol worked exactly as designed.
Implementation sequence
Discover and classify
Inventory SAP systems, client types, browser entry points, identity providers, directories, current login methods, trust stores and high privilege populations. Classify each access path as interactive user access, propagated user access or technical service access.
Design trust and mapping
Document the identity source, authentication method, token or certificate, trust anchor, mapping attribute, SAP account and authorization boundary. Include validity, renewal, revocation, fallback and monitoring in the design rather than leaving them for operations.
Prove the complete path
Test successful authentication, rejected authentication, expired credentials, incorrect mapping, revoked access, identity provider outage, certificate rollover and recovery. Include direct application server access, message server access, deep links and any alternate client route that users can reach.
Pilot with representative users
Select users across roles, locations, devices and network conditions. Include administrators and support staff. Measure login success, time to access, support demand, fallback use and mapping errors. A pilot is complete when it produces evidence for a rollout decision.
Transition to operations
Assign service ownership, alert handling, certificate or key rotation, client policy maintenance, identity mapping review and incident response. Publish a recovery process that does not weaken the control model during pressure.
Operations and troubleshooting
Troubleshoot from the user toward the backend. Confirm which credential the client selected, whether it is valid, whether the target name matches, whether the trust chain is complete and whether the external identity maps to the intended SAP user. Then confirm authorization and session creation. Changing several variables at once makes diagnosis slower and can hide the original cause.
Operational monitoring should cover failed authentication, repeated fallback, certificate issuance, certificate expiration, trust changes, mapping changes, service principal errors, time synchronization and unusual privileged access. Correlate timestamps across every component so one authentication journey can be reconstructed.
Migration and adoption
Move in controlled waves. Begin with a representative pilot, then expand by system, user population or location. Keep password fallback limited and measured during transition. A defined retirement date prevents the temporary fallback from becoming a permanent weak path.
User communication should explain what changes, what evidence may be requested, what happens on a new device and how recovery works. Support teams need diagnostic steps and secure recovery procedures before the first production wave.
Questions leaders should ask
Does the method match the access channel?
Confirm that the protocol is supported by the actual SAP client, application server, browser flow and system release. Do not assume that a browser federation method can directly replace SNC for desktop SAP GUI.
How is the identity mapped?
Require a one to one mapping that remains stable through employee and partner lifecycle events. Define who can change it and how that change is evidenced.
What happens when trust fails?
Plan for identity provider outage, certificate expiration, key rollover, domain disruption and client failure. Recovery must restore access without creating an uncontrolled bypass.
How will value be measured?
Measure password reduction, successful login rate, authentication time, support demand, privileged assurance, fallback use and control findings. These measures show whether the program improves both experience and security.
Cygnivo GUI SSO
Cygnivo GUI SSO provides a modern approach for SAP GUI authentication using enterprise identity, OAuth based authentication journeys and multi factor controls. It is designed to improve the user experience while preserving mapping, auditability and SAP access governance.
Explore Cygnivo products, review more SAP insights, or start a conversation with Cygnivo about your SAP authentication landscape.
About the author
Aaron
Enterprise transformation perspectives from the Cygnivo team.Put the insight to work